


Two critical vulnerabilities in PHP, a programming language used by roughly 70% of websites whose server-side technology is known, prompted government agencies and other organisations across Europe to take some services offline as a precaution. The flaws could allow remote code execution without authentication. Security teams urge operators to install the available updates immediately.
(Staff: Global & Europe / Technology & Cybersecurity)
Two critical flaws in PHP, a programming language that underpins a large part of the web, triggered an urgent security response on 21 October 2026. The vulnerabilities had gone undetected for years, and AI-assisted research helped turn a theoretical weakness into a working proof of concept.
PHP runs behind many websites and applications, including systems built with WordPress, Drupal and Joomla. W3Techs reported that PHP was used by about 69.7% of websites for which the server-side language could be identified in October 2026. That widespread use means a flaw in PHP can affect many different services.
Websites taken offline as a precaution
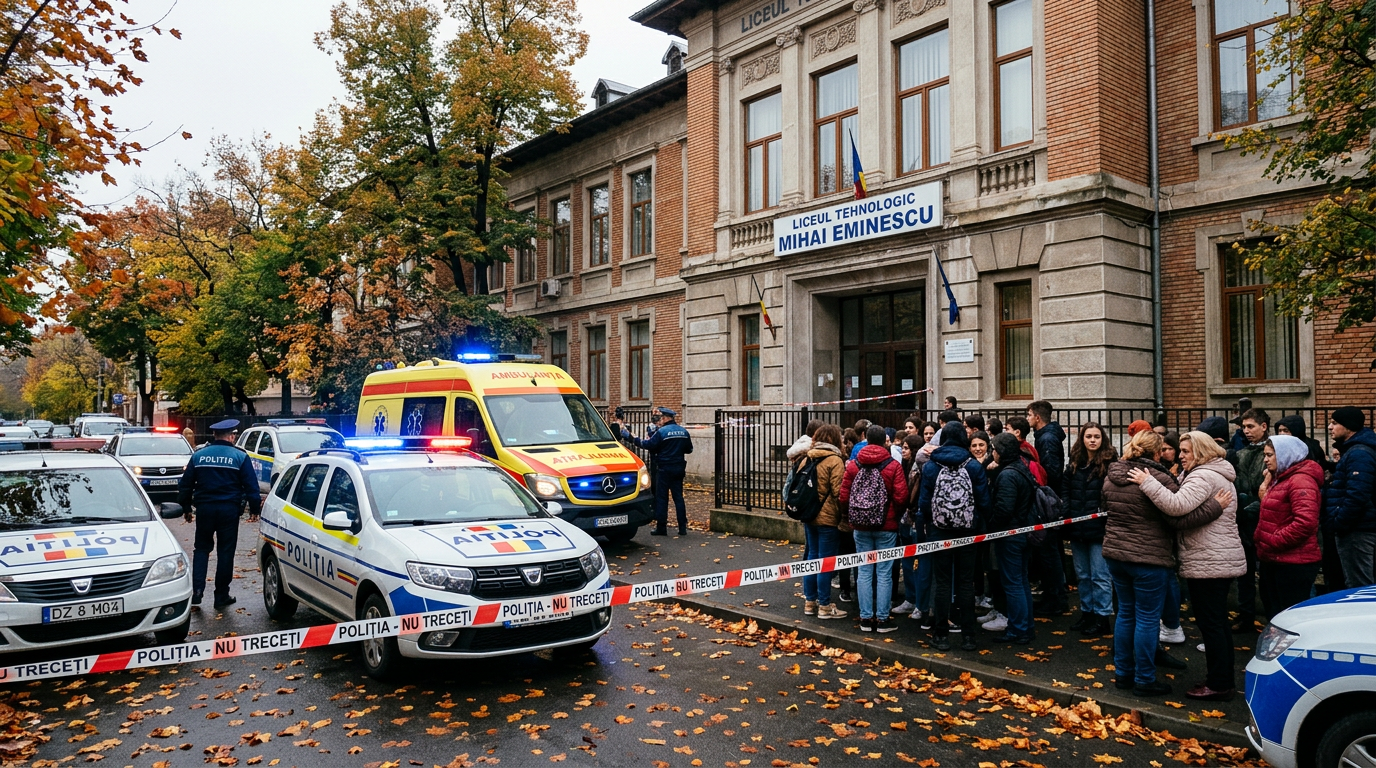
Authorities and organisations in several European countries temporarily disabled some public-facing services while preparing or applying security fixes. In the Netherlands, affected services included government portals and websites run by public institutions and other organisations. France, Germany and Finland also reported precautionary shutdowns. Taking a site offline does not itself mean that it has been hacked.
How AI helped identify the flaws
The vulnerabilities are tracked as CVE-2026-109618 and CVE-2026-109619 and have a severity score of 9.2 out of 10. They concern PHP memory handling and internal state, and could allow an unauthenticated attacker to execute code on a vulnerable server. Security firm Calif, during an OpenAI-funded audit of PHP source code, used OpenAI’s GPT-5.6 Sol model to develop a working remote attack based on one of the weaknesses. The discovery shows how AI can help security researchers analyse complex code, but similar capabilities could also help attackers.
A race to patch
The PHP team released security updates on 21 October 2026. Fixed versions include PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35; users should check the official PHP advisory and their operating-system or hosting provider for the appropriate update. Older versions may no longer receive fixes from the PHP project, although some vendors provide backported patches.
Censys data cited in reporting indicated that about 1.5 million of 2.6 million observed hosts were running PHP versions for which a fix was not available at the time of measurement. Cloudflare reported seeing attack traffic targeting customers, while agencies warned that public technical details could increase probing and exploitation attempts. The situation makes prompt patching particularly important for internet-facing systems.
What organisations should do
Organisations should identify every application and service that uses PHP, apply the relevant security update, and confirm that the patched version is actually running. If an exposed system cannot be patched promptly, cybersecurity agencies advise considering temporary isolation from the public internet. Website owners who use managed hosting should contact their provider to confirm that the fix has been applied.
Conclusion
The PHP incident is a reminder that widely used internet infrastructure needs continuous maintenance. AI-assisted analysis helped expose flaws that had remained hidden for years, while the public release of fixes has increased the urgency for administrators to secure vulnerable systems. The immediate priority is straightforward: verify the PHP version, apply the correct update and check that internet-facing services are protected.


Leave a Reply